
 Paladins & PriestsMods · 1.19 – 26.x
✨ Protect and heal your friends as a Paladin or a Priest
Gratuit3,554,122 téléchargements
TokenProtector prevents malicious mods from stealing your Minecraft session token. It sits between the game's authentication system and every mod in your…
Téléchargement direct depuis Modrinth · 22 téléchargements
Token Protector (mod) est une création de cev-api. TokenProtector prevents malicious mods from stealing your Minecraft session token. It sits between the game's authentication system and every mod in your…
Versions prises en charge : Minecraft 1.21 – 26.x. On compte 22 téléchargements sur Modrinth. La dernière mise à jour date du 09/09/2026.
Token Protector a publié 5 versions sur Modrinth depuis le 04/06/2026. 5 sont sorties au cours de l'année passée. La plus récente est 1.0.4, sortie le 09/09/2026. Elle est faite pour Minecraft 26.1 – 26.2. Elle fonctionne sur Fabric. Le téléchargement fait 134 KB.
| Version | Publié | Minecraft | Type |
|---|---|---|---|
1.0.4 | 09/09/2026 | 26.1 – 26.2 | Stable |
1.0.2 | 21/06/2026 | 1.21.1 – 1.21.11 | Stable |
1.0.2 | 21/06/2026 | 26.1 – 26.2 | Stable |
1.0.0 | 04/06/2026 | 26.1, 26.1.1, 26.1.2 | Stable |
1.0.0 | 04/06/2026 | 1.21.1 – 1.21.11 | Stable |
Token Protector est open source. Sa dernière version sur GitHub est Token Protector 1.0.5, publiée le 10/10/2026.
Avant : Token Protector 1.0.4 (09/09/2026), Token Protector v1.0.3 (14/07/2026).
TokenProtector is a client-side security mod for Minecraft 1.21.x and 26.x.
It reduces Minecraft access-token exposure to other Fabric mods. It replaces exposed token values with replacement data and reports blocked access when it can identify the caller.
Normal multiplayer, skins, and Realms continue to work because TokenProtector keeps the real access token only for the Minecraft authentication path that needs it.
TokenProtector protects these tested in-JVM paths:
Path · Tested result
User.getAccessToken() and User.getSessionId() · Replacement value
Direct User.accessToken field reads · Replacement value
Protected User and authlib fields read with reflection, Unsafe, VarHandle, or MethodHandle · Replacement value or access denied
User constructor HEAD capture · Replacement value
Maximum-priority User constructor Mixin · Replacement value
MinecraftClient.accessToken · Replacement value at rest
FabricLoader.getLaunchArguments(false) · Replacement accessToken
FabricLoader.getLaunchArguments(true) · Access token omitted
Tested authlib request hooks · Replacement value
High-speed token-field polling · Replacement value for the full test
Java-agent advice at raw Main.main bytecode entry · Replacement value
Tested HttpURLConnection auth-header probes · No Authorization value observed
Reflective read of the internal vault field (getDeclaredField("accessToken")) · No such field exists (credential is masked at rest)
Blind scan of static String fields for a JWT · No real token found
Retransformation targeting a single shared gate helper (authorized()) · No such helper exists (read gate is inline and duplicated)
TokenProtector sanitizes Fabric's retained launch arguments during Fabric preLaunch. Fabric builds the later Main.main(String[]) array from this retained data. As a result, the game receives the replacement token before normal Minecraft startup code runs.
TokenProtector also defends the internal state that holds the real token for authentication. The credential is never kept as a plaintext String: it is masked against a per-capture random pad and the plaintext is materialised only inside the gated read path at the moment it is handed to an authentication call. The read gate is performed inline in the accessor rather than delegated to a single helper method, so there is no authorized()-style choke point that a hostile retransformation could force to always allow.
TokenProtector is tested against TokenReader, a separate adversarial Fabric test mod (100+ probes across 13 categories). Every probe receives replacement data or nothing, and Minecraft authentication still completes:
Full details and technical limits are in WRITEUP.md.
TokenProtector is a hardening mod, not a sandbox. Its limitations:
While these are the limitations, most are still detected by the mod, just not blocked. This is because blocking them is outside what a same-JVM Fabric mod can enforce. Competing high-priority Mixins, preLaunch entrypoints, agent tooling, dynamic-attach artifacts, stripped protected classes, spin-races, and unexpected credential copies in environment variables, system properties, or process arguments all raise alerts. Only events that give no in-JVM signal at all, such as a launcher agent that runs before Fabric, native code, file copies, and network interception cannot be surfaced, and those are the true silent limits.
Full technical detail is in WRITEUP.md.
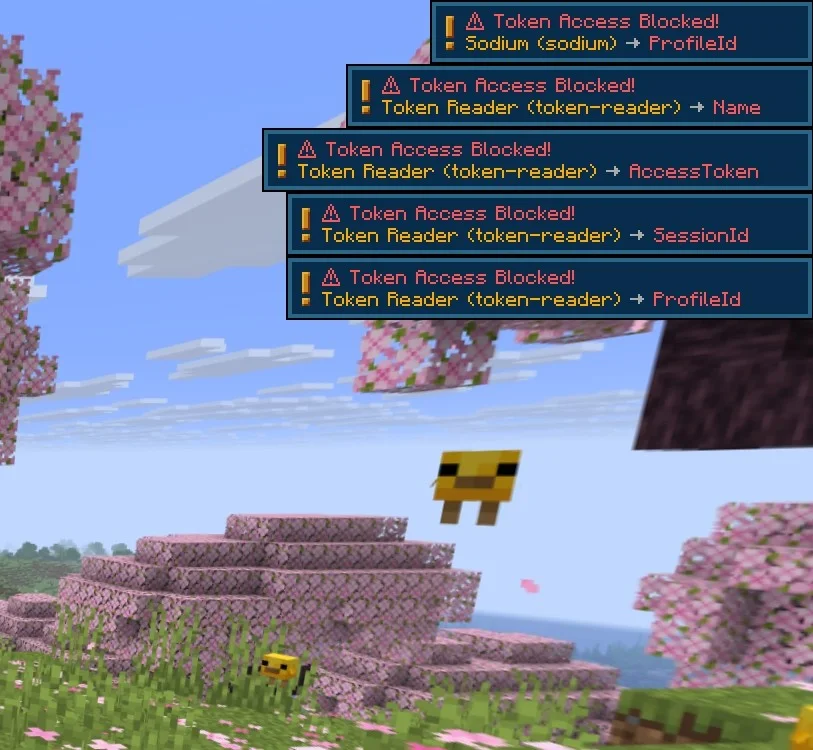
TokenProtector reports blocked caller-aware access (mod, class, method, line, field) and alerts on what it cannot block:
A warning means a possible credential is present in an inspected source; it does not prove another mod reads it. A single normal --accessToken launch argument is treated as expected exposure; warnings are for unexpected copies (duplicate tokens, --msaToken/--refreshToken, unknown JWT-shaped or wrapper-embedded values, long credential-like values, env/system-property leaks).
TokenProtector cannot rewrite the native OS command line, launcher files, launcher logs, or another process, and reports scans as incomplete when Java hides process data.
Every TokenProtector console line (INFO, WARN, ERROR, and ALERT) is recorded twice so it is never lost when the launcher console scrolls or closes:
Only ALERT lines increase the unread count shown on the top-right banner; INFO and WARN lines still appear in the in-game history and in the file.
Users who want to block the dynamic self-attach route used by tools such as Byte Buddy can add this JVM argument in the launcher:
-XX:+DisableAttachMechanism
This option must be present when Java starts. TokenProtector cannot enable it after the JVM starts.
It disables the JVM Attach mechanism used by dynamic self-attach. It does not stop a launcher-supplied -javaagent, native instrumentation, or a modified JVM or loader.
Use Mod Menu or edit config/tokenprotector.json.
Setting · Function
blockAccessToken · Replace the access token
blockSessionId · Replace the session ID
blockProfileId · Replace the player UUID
blockXuid · Replace the Xbox user ID
blockClientId · Replace the client ID
*Mode · Use FAKE, CUSTOM, or NONE
custom* · Set a custom replacement value
allowedMods · Allow selected caller-aware getter access
showToasts · Show protection alerts
showChatMessages · Show protection messages in chat
Only allow a mod when you trust it. An allowed caller-aware path can return real data to that mod.
Tested build targets:
For the technical design, adversarial test methods, and security limits, see WRITEUP.md.
Écrite par cev-api. À lire avec les images sur Modrinth.
Ce mod fonctionne uniquement dans ton jeu. Les serveurs n'en ont pas besoin, tu peux donc l'utiliser sur n'importe quel serveur.
Installe Fabric pour Minecraft 1.21 – 26.x.
Télécharge le fichier .jar depuis Modrinth et place-le dans le dossier mods de ton répertoire .minecraft.
Lance Minecraft avec le profil Fabric.
Plus simple : dans Prism Launcher ou la Modrinth App, cherche Token Protector dans les mods de ton instance et clique sur Install. Le loader et les mods requis sont ajoutés pour toi.
| Ressource | Téléchargements | Versions | Mise à jour | Prix |
|---|---|---|---|---|
| Token Protectorcelle que tu regardais | 22 | 1.21 – 26.x | 9 sept. 2026 | Gratuit |
| Paladins & PriestsZsoltMolnarrr | 3.6M | 1.19 – 26.x | 9 oct. 2026 | Gratuit |
 Offhand GuardInvisiblezappie | 6 | 1.21 – 26.x | 16 oct. 2026 | Gratuit |
 DonutSMP Session Profitsavxzthc | 41 | 1.21 | il y a 10 jours | Gratuit |
Oui. Token Protector prend en charge Minecraft 26.x. Toutes les versions prises en charge : 26.x, 1.21.
Oui. Token Protector se télécharge gratuitement sur Modrinth.
Côté client. Token Protector se place dans ton propre dossier mods et fonctionne sur n'importe quel serveur, même sans mods.
Oui. La dernière mise à jour date des dernières 24 heures.
Les plus proches sont Paladins & Priests, Offhand Guard et DonutSMP Session Profit. Comparer toutes les alternatives
Paladins & PriestsMods · 1.19 – 26.x✨ Protect and heal your friends as a Paladin or a Priest
Offhand GuardMods · 1.21 – 26.xProtect your offhand from accidental item swaps. Configurable allowed items, inventory protection, optional sound and a hold-to-bypass key.
DonutSMP Session ProfitMods · 1.21A draggable DonutSMP profit HUD with an animated aurora design, tracking your session from exact in game balance checks.
 Zhuravel ReminderMods · 1.21
A lightweight Fabric mod that adds a pinnable reminder note on your HUD, saved between sessions.
 StealthcraftMods · 26.x
Turn Minecraft into a stealth game, with entity vision cones, customizable interactions upon being seen and more.
 Simple Crash MenuMods · 1.16 – 1.21
Simply added a crash menu to prevent exiting game during crash.
Connecte-toi pour laisser un avis.